For insurance SIU and claims teams
Consistent delivery from every outside investigator.
When the investigators you assign use PIToolkit, your team gets one portal for case status, reports, evidence and messages, with every evidence file fingerprinted as it's uploaded. Free for clients.
PIToolkit is in development and not open to the public yet.
What your team gets
One portal across your vendors.
One sign-in across investigators
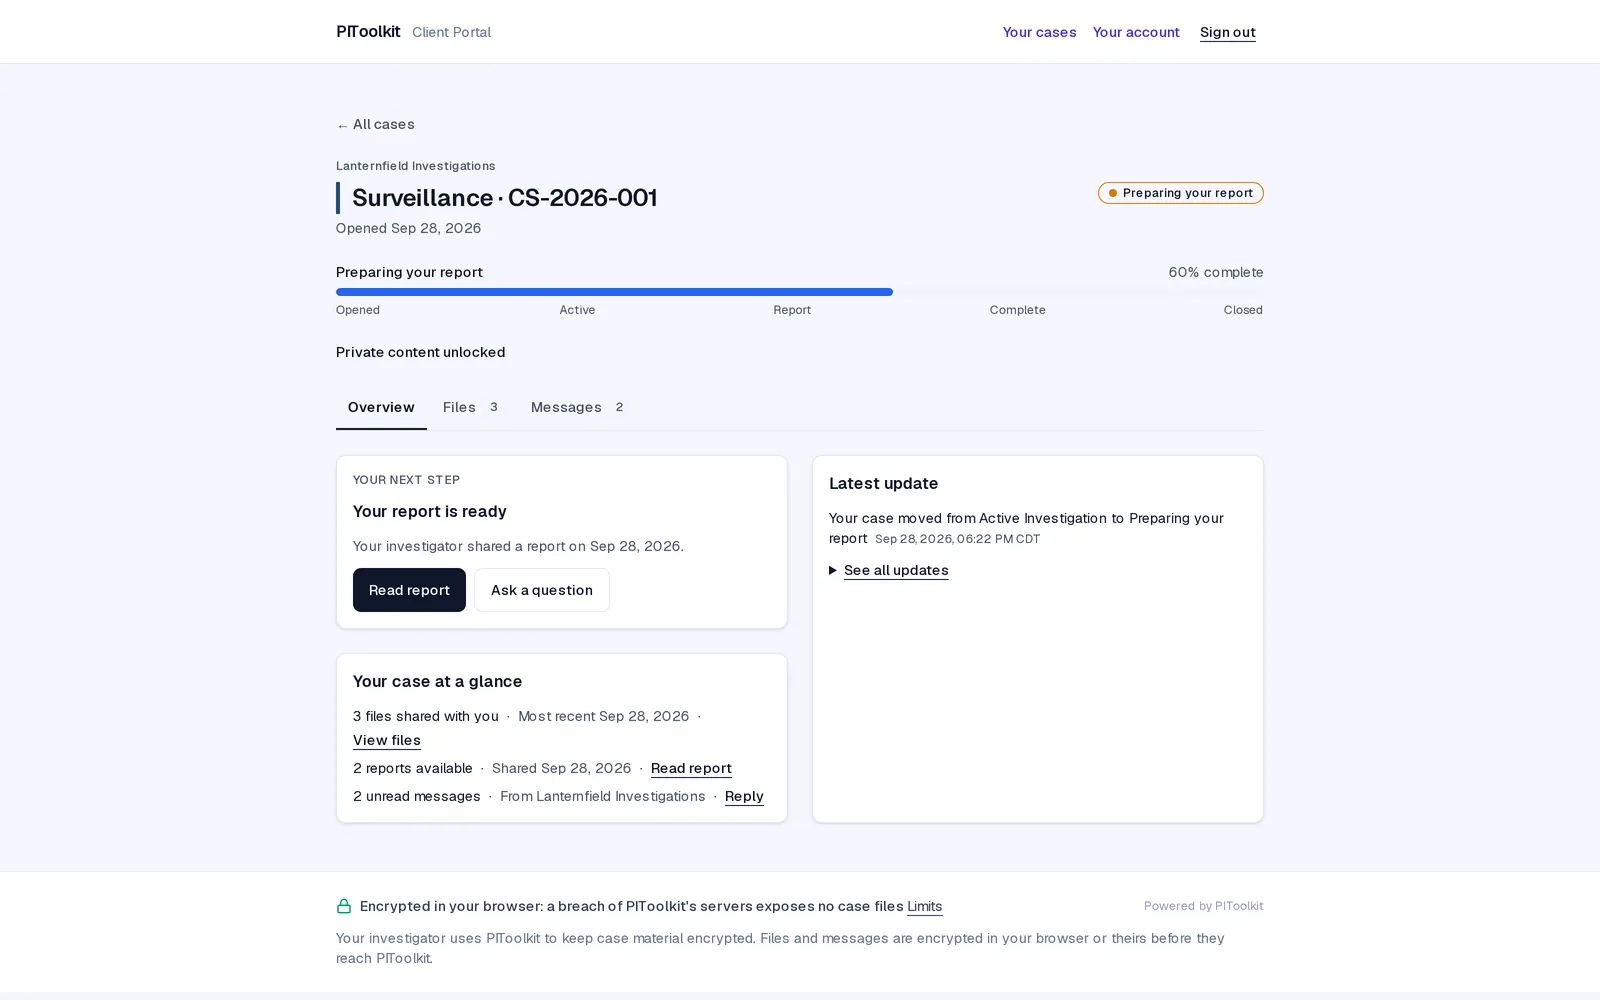
Adjusters and SIU staff see every case they've been invited to, from every investigator who uses PIToolkit, in one account. Each case keeps its investigator's branding, so it's always clear who did the work.
Status without chasing
Each case shows its phase, when it last changed, and a timeline of what the investigator has shared.
Reports and evidence together
Branded PDF reports and the evidence items the investigator releases to you, in one place, not across email threads and download links.
Messages on the file
Each case has its own encrypted thread with the investigator, so questions and answers stay with the case instead of in personal inboxes and phones.
Access that ends on schedule
When a case closes, the investigator sets how long client access lasts, and your team is told before it ends.
Evidence you can account for
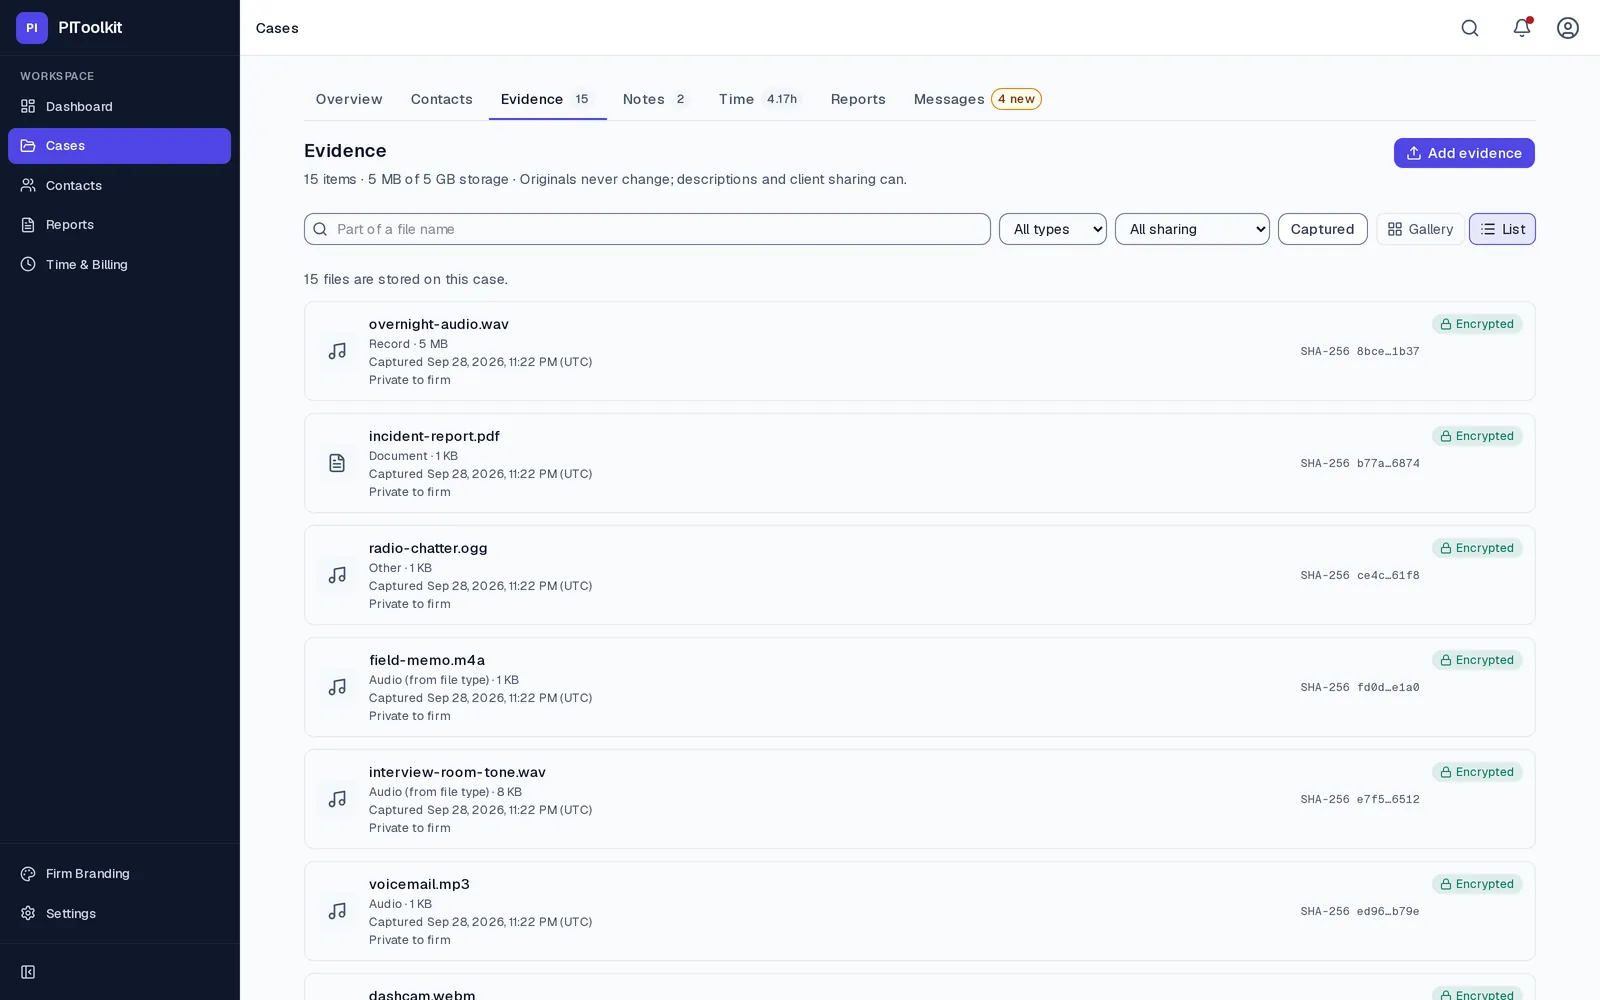
A record of each file, built as it's uploaded.
Every file gets a SHA-256 fingerprint in the investigator's browser, stored encrypted. Each item in a case is linked to the one before it, and the head of the chain is signed by the investigator, so someone with write access to our database can't alter or insert an item without the verification showing it. One limit today: someone who kept an older chain head the investigator really signed could put it back and cut off the newest items, and verification would still show the shorter chain as intact. Catching that is Planned.
Investigators can export an evidence package with the files, a verification report checking each against the chain, capture details and signatures. Ask for it when a file's history matters. Trusted third-party timestamping (RFC 3161) is Planned.
Why the architecture matters for claim files
Personal, medical and financial details, encrypted before upload.
Case material is encrypted in the investigator's browser and decrypted only in the browsers of the people they share it with. PIToolkit's servers store ciphertext, and our staff can't read case content.
If we're served with a demand, we can only produce what we hold: ciphertext, and the limited account and operational details listed on our security page.
For vendor-management and security reviewers
The gaps, before your questionnaire finds them.
- Who can decrypt case data?
- Only the investigator and the clients they share with. Decryption happens in the browser. Details
- What can PIToolkit see?
- Account basics such as sign-in email and plan, firm branding, operational details such as record type, size and dates, and a security log. Full list
- SOC 2 or ISO 27001?
- No. PIToolkit has no third-party certification, audit report or penetration test today, and we won't claim one until it exists.
- Two-factor for your staff?
- Available on every account with an authenticator app. Optional for client accounts, and we recommend it. Security keys are Planned.
- Can PIToolkit staff read case content?
- No. Our staff can't read case content, evidence or messages.
- Integration with claims systems?
- No.
- Data processing terms and sub-processor list?
- Planned Published before PIToolkit opens to paying customers.
- Hosting?
- Planned In the United States, at launch.
- Security contact?
- security@pitoolkit.com
For an in-house team
Built for independent investigators today.
Team accounts, with shared cases and roles, are Planned. What's planned for firms. PIToolkit is software for private investigators and their clients. We don't perform investigations, and we don't analyse claims.
Ask your investigators to deliver through PIToolkit
It's free for your team, and there's a free plan for investigators.